The Software Supply Chain Attack Crisis in 2026: Why Trusted Software Is Becoming a New Security Risk
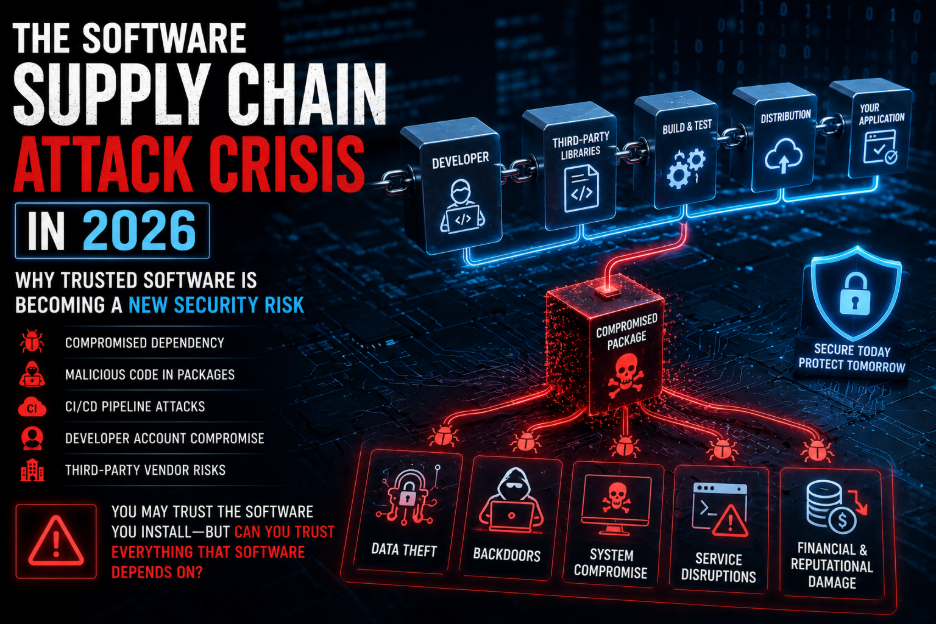
When organizations think about cybersecurity, they often focus on protecting their own servers, applications, networks, and employees. But modern software is rarely built entirely from scratch. A single application can depend on hundreds or even thousands of external components, including open-source libraries, third-party packages, cloud services, APIs, development tools, and software vendors. This creates a […]